Here is the uncomfortable question: if someone tricked you into typing your banking password into a fake site, how long would it take you to notice? For most people, the answer is long enough for the money to be gone. A passkey removes that failure mode, because there is no password to type anywhere.
A passkey is a cryptographic credential stored on your device or in a synced credential manager. It is built on the WebAuthn standard and uses public-key cryptography: your device generates two keys, shares the public one with the website, and keeps the private one to itself. When you sign in, the site sends a challenge, your device signs it with the private key, and the site verifies the signature with the public key. Your biometrics or device PIN never leave your hands.
That mechanism is why Microsoft's security explainer describes passkeys as resistant to phishing: there is no secret to be tricked into giving away, and an attacker would still need physical access to the device holding the private key. The catch is practical, not technical. Banks and brokerages have been slower to adopt passkeys than big consumer platforms, so most people still run a hybrid of passwords and passkeys today.
What exactly is a passkey, in plain terms?
Think of it as a replacement for the password field, not an extra lock. Instead of remembering a string of characters, you unlock the account the same way you unlock your phone: face recognition, fingerprint, or a PIN. The biometric check happens locally, on your device. The website never sees your face or fingerprint, only a signed mathematical response it can verify. Readers following this should also see How Palm and Face Payments Verify You at Biometric Checkout.
Two properties matter for financial accounts. First, the private key is bound to the site it was created for, so a credential made for your bank cannot be replayed to a lookalike domain. Second, a server holding passkey data holds only public keys. As the setup guide from Computer Techs Reno puts it, a hacked passkey database yields public keys that are useless without your physical device. That limits the blast radius of a breach on the bank's side.
Why does phishing resistance matter so much for banking?
Credential phishing is the cheapest way into a financial account. A convincing fake login page, a rushed victim, and the attacker has both the password and the one-time code you typed after it. Nothing about that flow works against a passkey. There is nothing to type, and the credential checks the domain it belongs to before it will sign anything.
Microsoft's overview also notes the reduced risk of account takeover: even if a passkey were somehow compromised, the attacker still needs the device it lives on to complete authentication. For a checking account, a payment app, or a brokerage, that possession requirement changes the threat model from "did I mistype something into the wrong site" to "does someone have my unlocked device," which is a much narrower question.
What happens when you enroll a passkey at a bank or payment app?
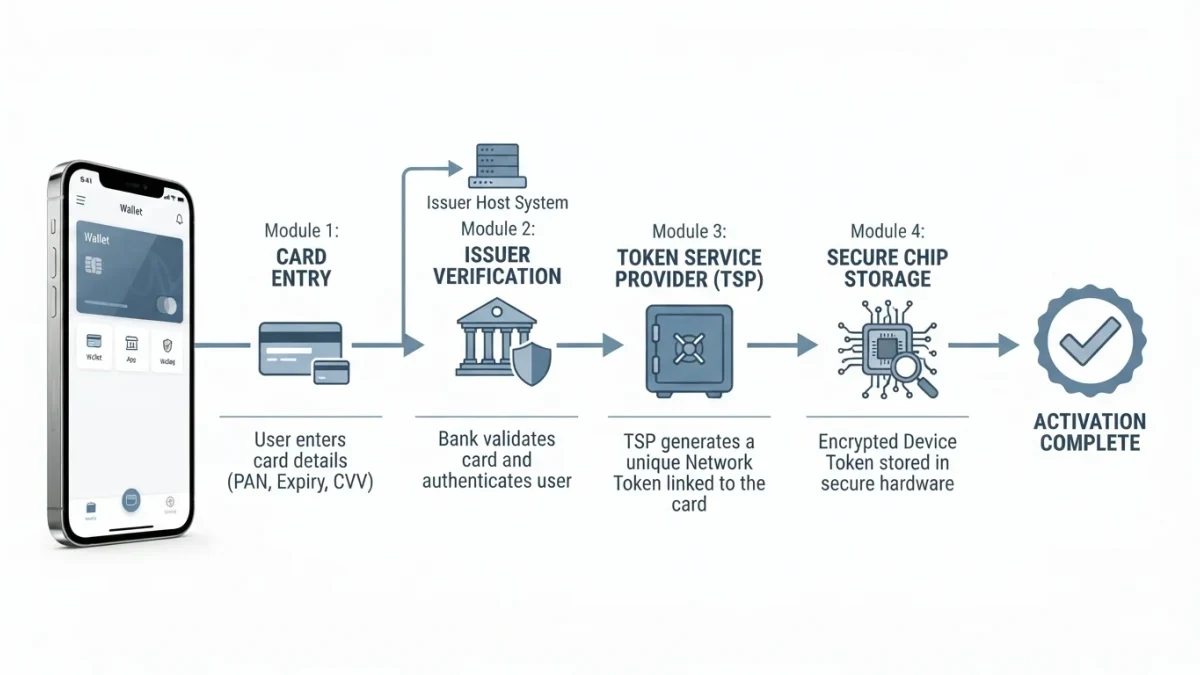
Enrollment follows the same pattern across sites, and Microsoft's step-by-step support page for creating and saving a passkey shows the flow in detail:
- Sign in to the account the normal way, with your password, one last time.
- Open the profile or security settings and look for a passkey option, then choose to create one.
- Pick where to store it: a synced credential manager such as Google Password Manager, Apple iCloud Keychain, or Microsoft Password Manager; the device itself through Windows Hello; or a physical security key.
- Confirm with your device unlock method, such as Face ID, fingerprint, or PIN.
Some flows add a wrinkle. Saving a passkey to a phone or tablet may require scanning a QR code with the mobile camera or Bluetooth pairing to verify the devices are close together. Some platforms also prompt for a recovery code during cloud sync setup, which you should store carefully, since it gates access to your synced credentials. We covered a connected angle in How Open Banking Consent Flows Secure Customer Data Access.
Device-bound or synced: which passkey fits a financial account?
The tradeoff sits between portability and containment. Neither choice is strictly better; they optimize for different failures.
| Attribute | Synced passkey | Device-bound passkey |
|---|---|---|
| Where the private key lives | Cloud credential manager, copied across your signed-in devices | One device or a hardware security key |
| Losing the device | Recover from another device in the sync chain | Locked out unless a backup credential exists |
| Attack surface | Includes your cloud account security | Includes only the physical device |
| Best fit | Everyday banking and payment apps | High-value accounts where a hardware key is warranted |
Synced passkeys solve the recovery problem. Microsoft's security overview notes that if you lose a device holding a synced passkey, you can use another device to regain access, because the credential moves with your cloud account. The limitation is obvious: the security of every synced passkey now depends on the strength of that cloud account, its recovery methods included. If someone defeats your Google or Apple account, they may inherit your credentials.
Device-bound passkeys invert the tradeoff. A passkey stored only on one device, or on a hardware security key, cannot be lifted from the cloud, but its loss is your problem. For a financial account, the workable answer is usually redundancy: a synced passkey for daily use, plus a backup credential, so a dead phone does not become a locked-out account.
What are the limits and open risks?
Passkeys do not make a bank account unstealable. They narrow one attack path, the phished password, while leaving others open. Social engineering at the support desk, SIM-swap attacks against SMS recovery, and malware on an unlocked device all still function. A passkey also inherits the health of the device holding it: a phone with no screen lock undermines the possession requirement entirely.
Adoption is the other limit. Major platforms including Google, Microsoft, Apple, and Yahoo support passkeys, and many large retailers do as well, but the same guides note that banks and brokerages have been slow to follow, so passwords remain in the picture for most people's money. Until a financial institution offers passkeys, the best available step is to use them everywhere they are offered and to protect the cloud account that would anchor any future synced credentials.
Our analysis: treat passkeys as infrastructure, not a product to buy. The mechanism is sound, the phishing resistance is real, and the failure modes, cloud-account compromise and single-device lockout, are manageable with a backup credential and a hardened recovery path. What remains unknown is how quickly deposit institutions close the adoption gap, and whether recovery flows at banks end up as strong as the login flows they replace.